
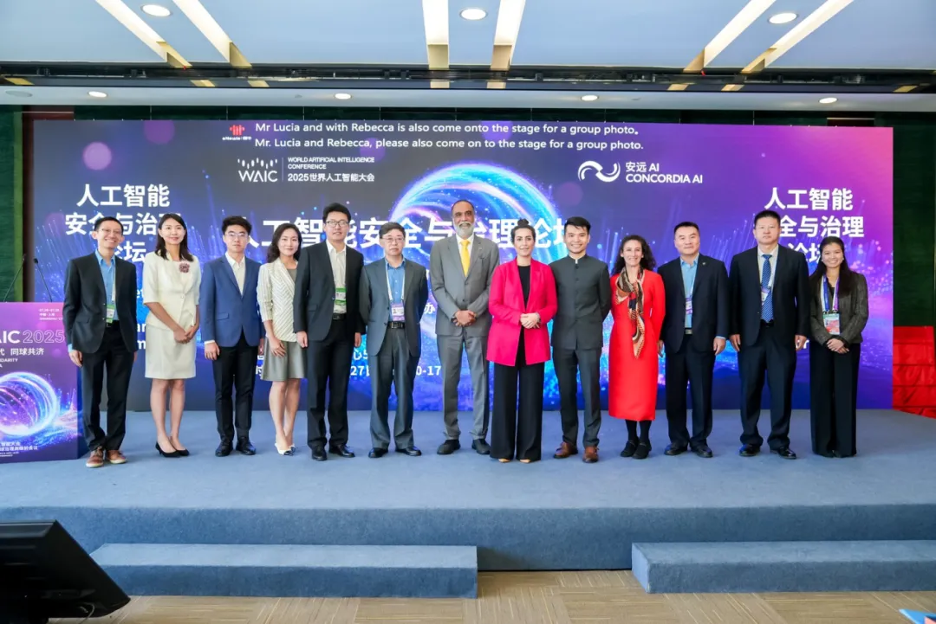
A Beijing-based AI safety group visited OpenAI’s SF headquarters last month to discuss international cooperation on AI risks, as the Trump administration weighs new disclosure requirements for US companies using Chinese-developed AI models.
A delegation from Beijing-based Concordia AI visited OpenAI’s San Francisco headquarters last month to brief technical staff and other employees on China’s approach to AI safety, as Politico reports. The organization also held meetings with technology companies in New York and Washington, along with appearances at an invite-only AI conference in Berkeley and events surrounding the United Nations General Assembly.
Concordia CEO Brian Tse and Kwan Yee Ng, who oversees the organization’s international AI safety and governance work, said the discussions were focused on Chinese AI research, safety concerns, and the possibility of coordinating international efforts to slow the development of increasingly powerful systems.
According to Politico, Google DeepMind has also participated in Concordia-hosted discussions, while Anthropic did not respond to requests for comment.
Ng said American researchers were particularly interested in whether China would consider slowing development of advanced AI systems if the US agreed to do the same, and how seriously Chinese technology companies and researchers viewed potential safety risks.
The discussions come as the US and nine allied countries have signed a new agreement aimed at securing the global AI supply chain against China. As SFist reported Monday, the San Francisco Declaration is part of a larger strategy to limit China's access to advanced AI technology, including semiconductors, while expanding cooperation among countries considered trusted partners.
Reuters reports that the Trump administration is considering a different approach to limiting American reliance on Chinese AI. The Treasury Department and White House Office of Science and Technology Policy have reportedly discussed requiring US companies to publicly disclose when they use Chinese-developed AI models, rather than imposing outright restrictions that could provoke industry opposition or anger Beijing.
The proposed disclosures could reportedly include posting the information on company websites.
The idea reflects growing concern about inexpensive Chinese open-weight models, including Alibaba’s Qwen, DeepSeek, and Moonshot AI’s Kimi, which American companies are increasingly adopting, per Reuters. Airbnb, for example, uses Qwen for its AI customer service agent, while coding tool Cursor, has used a version of Kimi. Both companies are SF-based.
According to the site Dark Reading, Cursor was recently involved in a security breach, where attackers exploited an access key exposed by third-party AI provider Fireworks that gave them access to Cursor user data and allowed them to distribute a malicious version of Anthropic’s Claude Code extension to as many as 5,000 users. The incident illustrates some of the risks associated with relying on interconnected AI services and third-party software providers.
Republican lawmakers Andrew Garbarino and John Moolenaar have reportedly launched an investigation into American companies' use of Chinese AI.
Meanwhile, Politico noted Tuesday that a string of recent technology failures has heightened AI security concerns. Outages and software problems affected Microsoft, JPMorgan Chase, United Airlines, Apple, the FAA, and the National Security Agency, which attributed its network disruption to routine maintenance.
Secretary of State Marco Rubio said there was no evidence connecting the incidents or suggesting they resulted from malicious activity. The affected companies and agencies also denied indications of cyberattacks.
Separately, Ars Technica reported Tuesday that security researchers discovered that malicious code had been inserted into JavaScript served through website personalization platform Optimizely, potentially exposing visitors to 178 websites, including CNN, Zoom, the BBC, and Salesforce. The code could reportedly steal cryptocurrency, payment card information, cookies, and screenshots, while delivering exploit kits capable of infecting iPhones and iPads.
Researchers have not established how attackers gained access to the affected customers or how many devices were successfully compromised.
[Update] Google also reported seeing AI-powered attack frameworks used against an aerospace company in the US and organizations across Asia, as well as a China-linked group developing automated tools for likely espionage, as CyberScoop reported Monday. The findings add to concerns that AI is lowering the barrier to cyberattacks while allowing hackers to find and exploit vulnerabilities at much greater speed.
Related: US, Allies Sign AI Pact In SF as Tens of Thousands Protest Proposed Tech Hub In Philippines

Join the conversation
Comments
Comments load automatically as this section approaches.